

Can a simple health log turn into evidence against you? Millions of people use cycle tools daily to record symptoms, medication, and pregnancy intent. Recent enforcement, including an FTC settlement with Flo after reports that the app shared sensitive signals with Facebook, shows how easily personal information can leave your device.
Data from popular services — Flo’s 43 million active users and Clue’s 12 million monthly users — highlight scale. When analytics or advertising SDKs export details, that information can be subpoenaed, sold, or combined with location pings and search history to suggest reproductive health choices.
This introduction outlines what the article will examine: what these services collect, how data flows off your phone, the legal channels that can access it, and practical steps to reduce exposure. We’ll compare U.S. and EU rules and review apps noted by Consumer Reports for safer designs.
Key Takeaways
- Understand what leaves your device: sensors, analytics, and ad toolkits often transmit sensitive information.
- Legal exposure is real: subpoenas, warrants, and modern geofence methods can target stored or shared data.
- Not all protections are equal: GDPR often gives stronger safeguards than U.S. laws like HIPAA in this area.
- Safer choices exist: prefer local-only modes, disable cloud backups, and reduce app permissions.
- Real cases matter: the FTC action against Flo shows policy language and actual data flows can diverge — see reporting from BBC News.
Why privacy concerns spiked after Roe v. Wade was overturned
The overturning of Roe v. Wade changed how everyday app logs and search histories are viewed by courts and private litigants. That shift made routine digital footprints far more consequential for many people.
From Dobbs to today: how shifting abortion laws changed the data risk calculus
The Dobbs decision ended federal protections and left states to set their own rules. At least 26 states moved toward bans, and some enacted harsh penalties—Missouri banned nearly all abortions, while Louisiana advanced bills equating abortion with homicide.
Legal changes plus statutes like Texas SB 8, which allows civil suits with steep fines, mean that digital traces can be used as evidence. Experts warn that purchase, subpoena, or aggregation of app and search records can point to reproductive choices.
Who is most exposed: users in states with criminalization or civil enforcement
Users in states with civil enforcement or criminal bans face higher exposure. But ad-tech markets and interstate data sharing can spread risk beyond borders. Company policies can change, and promises may be tested by subpoenas or public pressure.
Research and policy analysis now examine how post-Dobbs law interacts with commercial surveillance. The practical takeaway: if you live in or travel to banning states, reassess which apps and settings you trust and how your device sends data.
What period trackers collect and why it matters
Small inputs add up: a few symptom entries and a note on intent can form a persistent data trail. That trail mixes sensitive health signals with technical identifiers, so seemingly minor entries can carry outsized consequences.
Highly sensitive reproductive health signals
Cycle timing, symptoms, sexual activity, and pregnancy intent are core fields many users log. These entries create a longitudinal record of reproductive health that can show patterns over months or years.
Some apps request personal information like email or birthdate to enable accounts and backups. That expands how user data and health data can be tied to a real identity.
The metadata trail
Even without explicit identifiers, metadata—IP addresses, device IDs, and server timestamps—can link logs to devices and locations. Third‑party analytics commonly collect these signals for marketing.
When combined, direct entries plus metadata let companies infer missed cycles, clinic visits, or pregnancy. Evaluations using tools like THESIS show wide variation in how apps handle this information.
- What is collected: cycle dates, symptoms, notes, and account details.
- What connects entries to people: IP addresses, device identifiers, and emails.
- Why it matters: analytics and SDKs may export data used for advertising or research, expanding exposure.
| Data type | Example | How it links to identity | Why it matters |
|---|---|---|---|
| Health signals | Cycle start/stop, symptoms | Pattern matching over time | Reveals reproductive health trends |
| Account info | Email, DOB | Direct personal identifier | Enables account recovery and subpoenas |
| Metadata | IP, device ID, timestamps | Forensic linking to device/location | Infers clinic visits or missed cycles |
| Analytics data | Feature usage, event logs | Behavioral profiling | Valuable to advertisers and brokers |
For a deeper review of app practices and independent testing, see Consumer Reports’ evaluation of several popular services: consumer report on tracker design.
How your data moves: third parties, tracking, and resale
A single event can trigger multiple handoffs, moving data from a device to many servers. This section explains how embedded toolkits and ad networks push user data beyond the original app and why that matters for reproductive health entries.
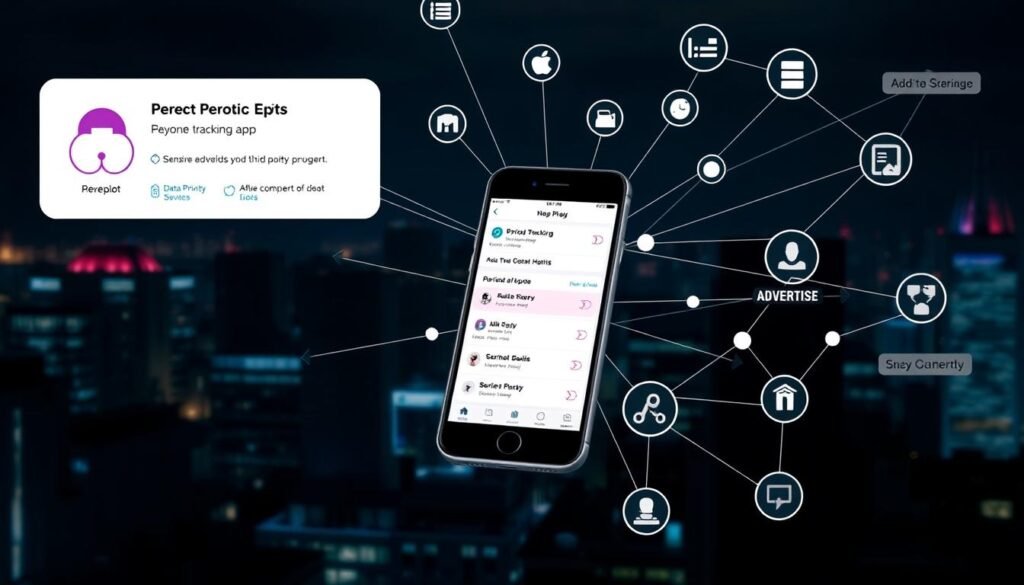
Third-party SDKs and analytics: when app data leaves your phone
Analytics and advertising SDKs can send event data, device identifiers, and engagement metrics off your phone by default.
Even a lightweight library like Firebase can export timestamps or feature events that, combined over time, reveal sensitive patterns.
From ad tech to data brokers: the path of user data beyond the app
Once data reaches third parties, it can move through ad-tech pipelines and brokers. Copies multiply and deletion becomes difficult.
“User data may reach many third parties and be resold, making it hard to track its eventual destinations.”
Consumer Reports found some apps avoid third-party trackers entirely, while others include one or more SDKs. That distinction matters.
Why transparency policies alone may not reveal the full picture
Privacy policies often list categories instead of precise flows. A company policy can claim no sale, yet allow broad transfers under service-provider exceptions.
To reduce exposure, prefer apps evaluated for no third-party trackers and limit features that require network access or accounts. Periodic checks of settings and updates help too.
- Key actions: pick vetted apps, disable unnecessary sync, and review permissions.
- Watch for changes: SDK updates can alter data paths without clear policy updates.
| Stage | Example | Why it matters | Mitigation |
|---|---|---|---|
| In-app SDK | Analytics events, Firebase | Sends identifiers off-device | Choose local-first apps; limit network features |
| Ad tech | Ad exchanges, retargeting | Profiles and cross-site linking | Block third-party cookies; use tracker blockers |
| Data broker | Aggregators selling segments | Hard to delete or trace copies | Prefer vendors audited by independent reviews |
| Downstream partners | Resellers, analytics partners | Unpredictable resale and reuse | Review policy changes and app disclosures |
For investigative reporting into these flows and enforcement examples, see reporting from independent health news.
Enforcement and subpoenas: when law enforcement comes knocking
Law enforcement often finds server-held records easier to obtain than files kept only on a personal device. This difference shapes what kinds of records investigators can access and how easily they can use them in cases.
How subpoenas and warrants differ
Subpoenas can compel companies to produce cloud-stored logs, backups, and account records without the higher probable-cause standard a warrant requires.
By contrast, officers usually need a warrant to search a user’s phone or local files. That legal threshold matters when deciding what evidence is available.
Geofence and keyword orders: wide nets, narrow targets
Geofence warrants ask companies to list devices in a defined location and time window. They can sweep up unrelated visitors, including clinic staff or passersby.
Keyword orders ask platforms to surface searches or queries that match terms of interest. Ordinary research can be implicated by these requests.
“Centralized backups create records that are easier for investigators to request than data kept only on a single phone.”
- Practical steps: disable cloud sync, prefer local-only storage, and limit account-linked backups.
- Note: transparency reports vary; many app policies do not disclose when companies hand over records.
Period Tracking Apps Privacy Risks in the United States
State laws and private enforcement have transformed ordinary digital logs into potential evidence in civil suits. This creates overlapping civil and criminal exposure for many people who record reproductive health details.
Private lawsuits and criminal probes now rely on digital traces that once seemed routine. In Texas, SB 8 allows private citizens to sue people who assist abortions with a minimum $10,000 penalty. Missouri and Louisiana have pursued strict criminal rules that raise the stakes.
How civil and criminal threats differ
State bans plus private enforcement create dual exposure: civil claims from private actors and potential criminal investigations by authorities. Combined logs — app entries, messages, and searches — can build a narrative of intent or assistance.
- Cross-jurisdiction effects: traveling or communicating across states complicates which law applies to your digital trail.
- Policy promises vs. reality: company statements may oppose subpoenas, but technical absence of server data matters most.
- Harm reduction: use local storage, pseudonyms, and disable cloud sync when feasible.
| Exposure | Example | Practical step |
|---|---|---|
| Civil suit | SB 8 bounty claims | Limit shared accounts; delete extraneous logs |
| Criminal probe | State felony statutes | Prefer local-only features; avoid identifiable accounts |
| Third-party resale | Brokered datasets | Choose services audited for minimal data flows |
FTC scrutiny and app privacy policies in flux
The federal trade commission has signaled that documentation matters: what a company promises in its privacy policies must match its technical practices. That enforcement changes how developers design backend systems and what users can expect about their personal information.
What the Flo settlement required and why it matters
The FTC settled with Flo after allegations the app misled users about sharing with third parties. Flo agreed to independent reviews and to obtain explicit consent before sharing certain records.
This action shows regulators will require audits, clear consent, and corrective measures when policy language diverges from practice.
What “privacy nutrition labels” can — and can’t — reveal
Apple’s labels give a quick snapshot of categories of data an app may collect. They help users compare services at a glance.
But research warns labels and privacy policies do not always map SDK behaviors, downstream brokers, or resale. Many companies still rely on remote storage to power predictions and sync features, keeping large server-side datasets.
“Disclosures are useful, but architecture—local-only storage and minimal third-party trackers—offers stronger protection than words alone.”
- Check design: prefer apps that minimize networked data by default.
- Demand transparency: favor companies that publish audit reports or transparency reports.
- Know the tradeoffs: cloud features can improve convenience but increase how widely data moves.
Local storage vs. cloud: which designs protect users best
Choosing where your entries live—on-device or in the cloud—shapes legal exposure and who can access those records. Local-only designs keep sensitive entries on your device and reduce how many copies exist outside your control.
Local-only storage: limiting legal exposure and third-party access
Local storage shrinks the surface for subpoenas, breaches, and resale. If a company never receives the data, it cannot hand it over or be breached on that record.
Consumer Reports highlights that local-first apps are inherently safer because they limit server-side holdings. Euki’s model, which lacks remote storage capacity, is an example of this approach.
Cloud dependence: predictions, sync features, and expanded data risk
Cloud features—predictions, sync, and restore—require server-side copies that increase access points for data. Backups, analytics logs, and partner infrastructures create multiple places where health data may sit.
For higher-risk users, prefer tools that work without accounts and disable auto-sync. Check the app’s policy and settings to confirm whether data can be encrypted at rest and whether analytics are optional.
- Practical: disable cloud backups and auto-sync on both the app and operating system.
- If you must use cloud: minimize fields you fill, avoid notes about intent, and verify encryption claims.
Which apps fared better in independent reviews
Independent testing found a few tools that favor local storage and minimal external code. Those designs lower how often your entries leave the device and reduce server-held copies that companies might be asked to disclose.
Drip, Euki, Periodical: local storage and no third-party tracking
Consumer Reports highlighted Drip, Euki, and Periodical for keeping records on-device and avoiding third‑party trackers. That approach reduces the chance that sensitive data is shared beyond the service.
Euki cannot store remotely without a major rework, which gives a predictable protection model. Periodical’s model is local-first but was not available on iOS at the time of review. Drip released an iOS version more recently.
Trade-offs and caveats
Not all options are server-free. Lady Cycle used a single Firebase analytics tracker, a middle ground that still creates external flows. Fertility Friend keeps minimal remote fields to enable sync and speeds up deletion to under seven days.
Across the sample, none of the eight services published transparency reports. That gap makes it harder to confirm how companies respond to legal requests.
| Service | Local-first | Third-party trackers | Notes |
|---|---|---|---|
| Drip | Yes | No | iOS release added; local storage prioritized |
| Euki | Yes | No | Cannot shift to remote storage without re-architecting |
| Periodical | Yes | No | Strong local model; limited platform availability then |
| Lady Cycle / Fertility Friend | Partial | One tracker / limited remote sync | Illustrates trade-offs: analytics vs. sync convenience |
Before choosing a period tracker, confirm current policy details and check recent research or consumer reviews to verify whether any clause could broaden data sharing.
It’s not just period apps: the broader digital footprint
Your phone collects more than you expect, and those small bits can be combined to tell a story. Even if you avoid certain health tools, unrelated services may log location pings, searches, and browsing that reveal sensitive movements.
Multiple background services often capture tiny signals that, when merged, form a clear pattern. Evan Greer notes that unrelated apps running near clinics can record location data that maps visits.
Ad-tech ecosystems link location, device IDs, and browsing to build profiles. Geofence warrants then let law enforcement ask companies which devices were inside a radius and time window.
Search queries, browsing data, and targeted advertising
Lydia X. Z. Brown warns that search histories and browsing can be bought or subpoenaed and used for predatory ads or citizen reporting under laws like Roe v. Wade-era statutes.
- Practical steps: turn off precise location for nonessential apps and prune permissions.
- Use private browsing, privacy-focused search engines, or separate profiles for sensitive research.
- Review OS privacy dashboards to see which apps accessed location, camera, or mic recently.
“Your digital footprint extends well beyond any single app, so comprehensive hygiene matters.”
Practical steps to reduce your risk right now
Take simple, concrete steps to limit how records leave your device. These changes cut copies of user data on servers and lower legal exposure for users who want stronger protections.
Prefer local-only tools and disable cloud backups
Choose local-only apps that work without accounts. Turn off OS and app-level cloud backups so copies do not sit on remote servers.
Share the minimum necessary. Skip optional fields and notes about intent. Disable location, Bluetooth, and background activity unless essential to core features.
Use pseudonyms, device hygiene, and offline options
If an account is unavoidable, use a unique email or pseudonym and avoid social logins. Keep a strong passcode, enable automatic updates, and use full-disk encryption on your phone.
For higher risk, keep records offline—paper calendars or air-gapped spreadsheets remove network access entirely.
- Check for trackers: use reputable tools to spot third-party trackers and disable analytics when possible.
- Revisit settings: export or delete data and confirm removals; verify connected services have no residual access.
| Action | Why it helps | Quick steps |
|---|---|---|
| Local-only choice | Reduces server-held user data | Pick tools without accounts; disable sync |
| Permission audit | Limits unwanted access | Turn off location/Bluetooth; remove unused apps |
| Pseudonym & hygiene | Severs easy identity links | Use unique emails; enable encryption |
U.S. vs. EU privacy frameworks: why protections differ
When data crosses borders, different legal defaults decide whether your health entries get strong legal shields or weak ones. This difference changes what rights users have, how companies must handle information, and how law enforcement can request records.
How GDPR protects sensitive health data
GDPR treats health data as a special category. It requires explicit consent, purpose limitation, and strict rules on profiling and transfers.
EU-based services such as Clue can rely on subscription models and stronger defaults for user rights and data minimization. That design makes it harder for third parties to reuse health data without clear legal bases.
Why HIPAA and U.S. rules often fall short
HIPAA generally does not cover consumer tools that are not run by covered entities. In the U.S., a patchwork of state laws and sector rules leaves many consumer services without baseline protections.
- Check privacy policies for retention, international transfers, and service‑provider exceptions.
- Prefer tools that minimize collection, store user data locally, and avoid third‑party trackers to approximate stronger EU protections.
Conclusion
Choose tools that keep records on your device and limit account-backed copies; design often protects better than promises. Practical steps—disable cloud sync, minimize entries, and prefer local-first offerings like Drip, Euki, or Periodical—shrink how much sensitive information exists.
Treat cycle logs, symptoms, and pregnancy intent as sensitive. Minimize notes and avoid optional fields that broaden exposure. If your exposure is high, consider offline methods such as paper logs until systems and laws stabilize.
Remember that search histories, location signals, and ad ecosystems can fill gaps beyond any single app. For longer reading and a deeper research review, see this research review.
Keep iterating: run permission audits, update credentials, and switch tools if a service adds third‑party toolkits. Small, consistent steps lower your overall risk.
FAQ
Why did concerns about reproductive app data rise after Roe v. Wade was overturned?
The Dobbs decision shifted legal landscapes in many states, making medical and reproductive information potentially relevant to criminal investigations or civil suits. That raised alarm because data from cycle-monitoring tools can be used as corroborating evidence when prosecutors or private plaintiffs seek proof of pregnancy outcomes or intent. Users in jurisdictions with restrictive laws are therefore at higher risk of legal exposure from data that apps collect or share.
What kinds of health and behavioral information do these apps typically collect?
Many apps gather cycle dates, symptoms, sexual activity, contraception use, pregnancy tests and intentions, mood, and medication records—details that reveal reproductive status and intent. Apps also often record metadata such as timestamps, IP addresses, device identifiers, and inferred fertility windows, which can be combined to build a detailed personal profile.
How does metadata make reproductive data more revealing?
Metadata like GPS, IP addresses, and device IDs links health entries to locations, times, and other online behavior. For example, a timestamped symptom entry plus location data near a clinic can strengthen inferences about care-seeking, turning seemingly innocuous logs into actionable evidence.
When and how does app data leave my phone?
Data can leave a device via third-party SDKs (analytics, crash reporting, ad networks), cloud backups and sync features, or through explicit sharing by the app developer. Third-party libraries often transmit aggregated or raw event data to external servers, which means your information can reside outside the app developer’s control.
Who are the typical third parties that receive user data?
Recipients include analytics firms (like Google Analytics, Mixpanel), advertising networks, cloud hosting providers, and data brokers. Once data reaches ad tech or broker ecosystems, it can be combined with other data sources and resold, making it difficult to track or retract.
Can privacy policies be trusted to protect users?
Privacy policies provide useful disclosures but often omit technical details about data flows, third-party access, retention, and resale. Policies may also change; enforcement by the Federal Trade Commission and settlements (for example, the Flo case) show that misleading or incomplete statements can be challenged, but policy text alone isn’t a guarantee of safety.
What legal processes can force apps or companies to hand over user data?
Law enforcement can use subpoenas, warrants, and court orders to obtain data from apps, cloud providers, or device backups. Subpoenas often demand basic account records, while warrants—supported by probable cause—can compel access to content stored on servers. The threshold and process vary by jurisdiction and whether data is held domestically or abroad.
What are geofence and keyword warrants, and why do they matter?
Geofence warrants ask providers for data about devices in a virtual area during a time window; keyword warrants target search or messaging records containing specific terms. Both can pull large datasets and have been used in investigations involving reproductive healthcare, making unrelated app location and search logs potentially relevant.
Are users in some states more exposed to civil lawsuits or criminal charges?
Yes. States that allow private civil suits related to reproductive conduct can expose users to liability based on digital traces. States with criminal restrictions on abortion or stricter enforcement may use app data as evidence. Risk is therefore uneven across the U.S., and users in restrictive jurisdictions face greater exposure.
Does HIPAA protect data from consumer health apps?
Generally no. HIPAA protects health information handled by covered entities like healthcare providers and plans, not most consumer apps. If an app partners directly with a covered entity in a way that creates a business associate relationship, some protections may apply, but most standalone reproductive health apps fall outside HIPAA’s scope.
How do U.S. privacy rules compare with the EU’s GDPR for sensitive health data?
The GDPR treats health data as a special category and requires stronger legal bases for processing, tighter consent rules, and data subject rights like deletion and portability. U.S. rules are more fragmented, with no single federal law offering equivalent protections for most consumer app data, creating a patchwork of state-level safeguards.
Can local-only storage and offline apps reduce legal risk?
Local-only designs that keep data on-device without cloud sync or third-party trackers lower exposure because there’s no central repository for subpoenas and fewer external recipients. However, local data can still be accessed through a seized device, so device-level protections like encryption and strong passcodes remain important.
What are the trade-offs of apps that avoid third-party tracking?
Apps that minimize tracking and store data locally offer better privacy but may provide fewer convenience features—cross-device sync, predictive models, or backups. Users should weigh privacy priorities against functionality and choose apps whose practices and feature sets align with their risk tolerance.
Which apps have been noted for safer designs, and what caveats apply?
Independent reviewers have highlighted apps such as Drip, Euki, and Periodical for local storage and minimal third-party tracking. Still, no app is perfect: some may use a single analytics service, offer optional cloud features, or include policy language that allows data sharing under certain conditions. Always review permissions and settings carefully.
Yes. Location pings from mapping, rideshare, or social apps and targeted ads can create a digital trail near clinics. Aggregated location and browsing data can be correlated and sold by brokers, so app behaviors beyond reproductive tools contribute to overall exposure.
What immediate steps can I take to reduce my exposure right now?
Prefer apps with local-only storage; disable cloud backups and account sync; limit permissions (location, microphone, contacts); uninstall unnecessary apps; review and revoke third-party trackers via privacy settings; use a different browser for sensitive searches or a privacy-focused search engine; consider paper or offline tracking if risk is high.
Are pseudonyms or fake data effective protections?
Using pseudonyms or vague entries can reduce the specificity of records but may break app functionality or violate terms of service. Pseudonymous use is a helpful tactic when combined with disabling sync and avoiding account creation, but it’s not foolproof against device seizure or network-level identifiers.
What role has the Federal Trade Commission played in app oversight?
The FTC enforces against deceptive practices and has taken action when apps misrepresent data uses, as in the Flo settlement, requiring audits and clearer disclosures. The agency can pursue penalties and corrective measures when companies breach consumer trust through misleading privacy claims.
Should I assume data deleted in an app is gone forever?
No. Deletion in-app may remove your view, but copies can persist in backups, third-party analytics, or server logs. Ask developers about retention policies and request data deletion under applicable laws or platform privacy tools. Complete removal can be difficult once data has been shared externally.
How can developers design apps to reduce user legal risk?
Best practices include defaulting to local storage, minimizing data collection to what’s strictly necessary, avoiding third-party trackers, encrypting stored data, providing robust deletion tools, and maintaining transparent, specific policies. Privacy-by-design choices materially reduce downstream exposure for users.
Where can I find independent research or audits on app privacy?
Look to nonprofit organizations like the Electronic Frontier Foundation (EFF), research from academic security labs, reports by the Center for Democracy & Technology, and consumer test results from privacy-focused outlets. Government resources and .gov guidance can also clarify legal risk and rights in your state.

Don’t Miss These Picks